Bitbait

Lure, detect, and analyse attackers

A modern honeypot and deception platform that poses as real IT, healthcare, and OT services inside your network. The moment someone touches one, you know exactly who they are, where they came from, and what they were after.

  • The first touch is already an alert
  • Almost no false positives
  • Production systems stay untouched
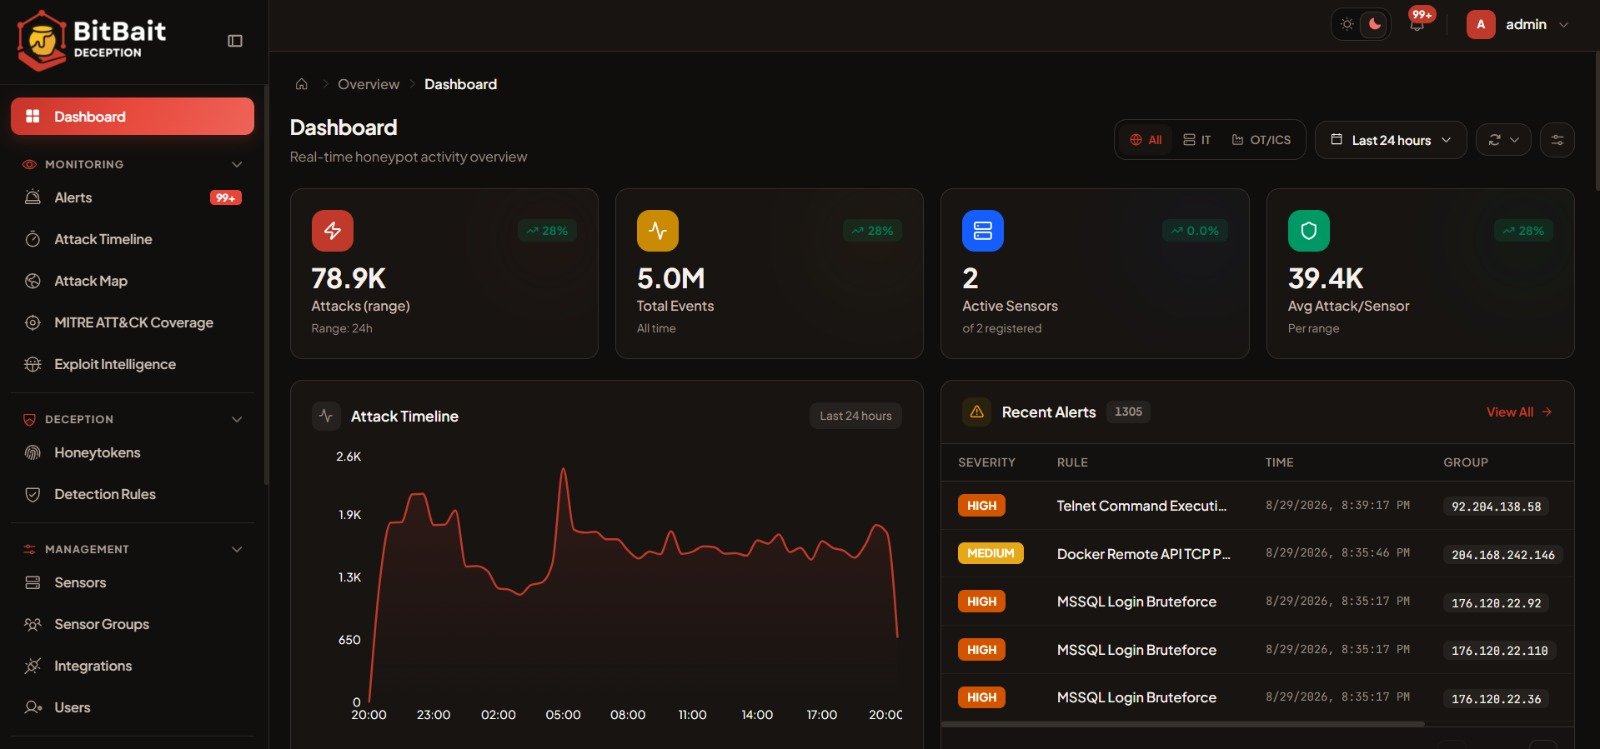
bitbait / dashboard
BitBait deception dashboard
42 Emulated services
13 OT and ICS protocols
8 Emulated web apps
2 MITRE ATT&CK matrices
01 / How it works

Catch attackers before they reach the real assets

No legitimate user has any reason to touch a decoy. That is why a single touch is enough to raise a warning worth trusting.

  1. 01

    Lure

    Emulates real IT, healthcare, and OT services so attackers spend their time on decoys instead of your systems.

  2. 02

    Detect

    Detects reconnaissance, credential theft, and exploitation attempts, recorded in full from the very first touch.

  3. 03

    Analyse

    Turns attack data into early warning and actionable threat intelligence your defenders can put to work.

02 / Emulation coverage

Forty two services across three different worlds

Office IT, hospital interoperability, and factory floor protocols. Each decoy imitates how a real service behaves, not just an open port.

IT services and protocols 26
05 services

Database services

MSSQL MySQL PostgreSQL Oracle TNS MongoDB
06 services

Remote access and network

SSH FTP RDP VNC Winbox Telnet
05 services

Directory, messaging, and sync

SIP LDAP SNMP SMTP NTP
04 services

Infrastructure and DevOps

Docker HTTP Kibana K8s API
06 services

Enterprise and legacy systems

Redis Printer IBM TN3270 SMB FGFM ASA IKE
Healthcare interoperability 3
FHIR

Modern web APIs

Fast Healthcare Interoperability Resources, the API standard hospital systems exchange records over.

HL7 MLP

Message transport

Health Level 7 Minimal Lower Layer Protocol, the transport that carries clinical messages between systems.

DICOM

Medical imaging

Digital Imaging and Communications in Medicine, the standard behind radiology images and modality traffic.

OT and ICS protocols 13
  • CODESYS PLC runtime
  • Triconex Safety controller
  • Siemens S7 PLC
  • MELSEC-Q PLC
  • OMRON FINS PLC
  • OPC UA Industrial data
  • Modbus Fieldbus
  • EtherNet/IP Fieldbus
  • DNP3 SCADA
  • IEC 60870-5-104 Telecontrol
  • BACnet Building automation
  • Tridium Niagara Building automation
  • Veeder-Root Tank gauge
03 / Special decoys

Two decoys that draw attackers out most often

Beyond the imitation services, Bitbait plants fake web applications and breadcrumbs inside your real environment.

HONEYPOT HTTP

Web appliances an attacker expects to find

The HTTP honeypot emulates the real world web applications and appliances attackers go for first. It is fully customisable, so a decoy can be crafted to match your own environment or industry.

  • Attackers believe they are facing a real system
  • Decoy pages can follow your own visual identity
  • Every login attempt is recorded along with its credentials
  • Jenkins CI server
  • Pulse Secure VPN gateway
  • Citrix NetScaler ADC
  • F5 Big-IP ADC
  • Fortinet Firewall
  • SAP NetWeaver ERP
  • Outlook Webmail
  • Oracle WebLogic App server
HONEYTOKEN AND BREADCRUMBS

Breadcrumbs inside the real systems

Fake keys, documents, and credentials are generated and planted on servers and file shares that are genuinely in use. No employee has any reason to open them, so once one is touched the signal almost certainly comes from an intruder.

  • High fidelity detection the moment a token is used
  • Planted across file shares, endpoints, and repositories
  • Maps how far the attacker has already moved
AWS key Excel Word PDF Map file Config file
04 / Detection and alerting

Every alert arrives mapped and ready to act on

Reconnaissance is caught early, notifications are enriched with context, and each one is tied to MITRE ATT&CK Enterprise and ICS.

Early reconnaissance 2

Port scan detection

Scanning attempts against the decoys are caught while the attacker is still mapping the network.

Responder activity detection

Poisoning of name resolution traffic is flagged, one of the earliest signs of an intruder inside the LAN.

Alerting and ATT&CK mapping 3

Real time alerting engine

Suspicious activity is reported the moment it happens, not in the next daily report.

MITRE ATT&CK mapping

Every alert is tied to a tactic and a technique, available for the Enterprise and the ICS matrix alike.

Detection logic you can extend

Rules can be created and adjusted to match your environment and your own threat model.

05 / AI assistance

Investigation summaries in a matter of seconds

The assistant summarises the threat, its risk, and its MITRE mapping, reconstructs the attack timeline with IOC extraction, generates executive insight, and answers questions against live data. Analysts still hold the decision; it is the manual work that shrinks.

  • Threat and risk summary
  • Attack timeline
  • IOC extraction
  • MITRE mapping
  • Executive insight
  • Chat with live data
Model providers and MCP 7
  • OpenAI
  • Claude
  • Gemini
  • Ollama
  • DeepSeek
  • Groq
  • Mistral AI

Context aware analysis over MCP, self hosted models included

06 / Integration

Findings flow into the defences you already run

Nothing needs replacing. Alerts leave as structured intelligence and land in the firewalls, SIEMs, and chat channels already in place.

04 formats

Threat sharing

Alert data is exported as structured threat intelligence, ready for external CTI platforms.

STIX TAXII MISP IP reputation
05 channels

Alert channels

Real time alerts land in the tools your team already lives in, for collaborative incident response.

Slack Telegram PagerDuty Discord Webhook
CTI and defensive systems 10
  • Palo Alto Networks Firewall
  • Fortinet Firewall
  • Check Point Firewall
  • pfSense Firewall
  • Cisco Network
  • MikroTik Router
  • F5 ADC and WAF
  • Elastic SIEM
  • Splunk SIEM
  • Azure Sentinel SIEM
Total 42 emulated services

Picked to match your environment and sector

07 / Get started

Plant your first decoy this week

We will help you decide which services make the most sense as bait in your network, then walk you through the flow from the first touch to the report.

  • Answer within one working day
  • NDA available before the demo
  • No changes to production systems
WHATSAPP